
Report: US Coast Guard's SASH Prevention Programs Lack Unifying Framework
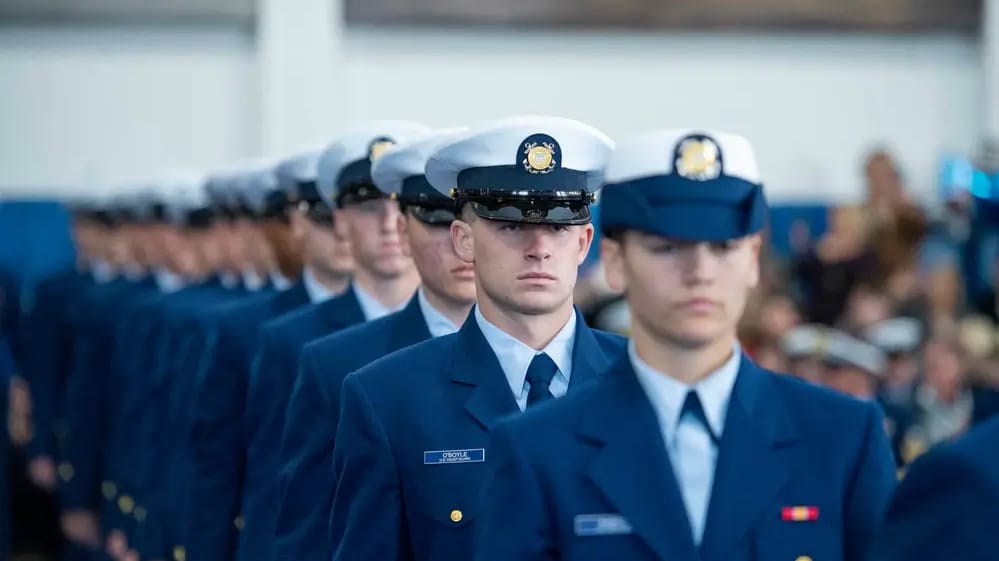
Rand released a report earlier this month entitled “Sexual Assault and Sexual Harassment in the Coast Guard.” The report was mandated by the Fiscal Year 2024 Department of Homeland Security Appropriations Act, which directed the Secretary of Homeland Security to charter an independent and impartial review of the service’s efforts to reduce and respond to sexual assault and sexual harassment.
Additionally, Congress directed that the review evaluate past and present climate and culture, preventative measures, accountability, transparency, victim support, and awareness; identify and evaluate completed and ongoing efforts and reforms undertaken to improve these areas; and make recommendations for additional efforts and reforms that should be undertaken to close remaining gaps.
RAND researchers found a SASH policy environment characterized by distributed authority without centralized integration. Although individual programs address distinct forms of harm, the absence of a unifying framework limits the Coast Guard’s ability to monitor implementation, assess outcomes across programs, and ensure consistent experiences for victims and practitioners. They examined how these structural features influence prevention effectiveness, response quality, and accountability in practice.
The RAND report noted that slow case timelines and limited transparency erodes trust. One of the Special Victims Counsel who spoke with researchers shared:
"The biggest issue my clients face is that they make the decision to come forward and report, and then they’re stuck in limbo for a very long time. That uncertainty and feeling of powerlessness, because someone else is making a decision, eats away at them. They just want a decision made one way or another to get closure from these events. The lengthy time for prosecution in the Coast Guard negatively impacts victims."
Key Takeaways In the RAND Report
- The Coast Guard’s SASH efforts are constrained less by an absence of programs than by how those programs are structured, integrated, and resourced.
- The most foundational concerns involve fragmented policy architecture and data. SASH-related policy is distributed across three distinct directives, with no single integrating framework.
- Data on SASH incidents are similarly fragmented across multiple tracking systems with differing definitions and reporting standards, which limits the Coast Guard’s ability to assess trends, evaluate what is working, and identify where risk is concentrated.
- Prevention and leadership present related challenges. The Coast Guard’s prevention activity is largely training-centric, with success measured by course completion rates rather than demonstrated changes in behavior or risk.
- The response and support system faces ongoing challenges. Survivors and stakeholders expressed continued concern about long investigative timelines, limited visibility into case status, and inconsistent communication.
- Quantitatively, official sexual assault reporting rates have been relatively stable in recent years, but survey-based estimates of prevalence consistently exceed official report counts, indicating that underreporting remains a significant concern.
RAND Report Recommendations
- Fragmented policy architecture limits coherence, clarity of authority, and accountability. One option would be to establish a single authoritative instruction consolidating SASH prevention, response, recovery, and accountability; another would retain the existing program-specific instructions while introducing a formal governance body to coordinate them and track implementation.
- Prevention is treated primarily as training compliance rather than as a sustained capability. One option would reframe prevention as an enterprise capability with measurable outcome targets; another would require individual programs to articulate how their activities reduce risk.
- Variable training quality, consistency, and focus limit prevention effectiveness. One option would establish a tiered model based on unit risk; another would build risk-based triggers into existing policy.
- Commanders are expected to foster safe and accountable unit climates, but policy provides limited behavioral specificity and no structured accountability mechanisms. One option is to articulate specific behavioral expectations for leaders in policy and to reinforce those expectations through professional development and evaluation.
- Response systems have improved, but trust remains fragile due to communication, transparency, and timeline challenges. One option is to standardize communication practices across the response system; another would focus on reducing investigative timelines through process improvements.
- Resource constraints create a reactive system with limited capacity for prevention and sustained engagement. One option would assign new billets or assignments based on risk and geographic access; another would expand capacity through augmentation strategies.
that matters most
Get the latest maritime news delivered to your inbox daily.
- Data fragmentation and governance challenges limit evaluation, oversight, and organizational learning. One option would move toward an integrated data environment; another would clarify data stewardship and improve interoperability across existing systems.
K. Denise Rucker Krepp is a Coast Guard veteran and former Maritime Administration Chief Counsel.
The opinions expressed herein are the author's and not necessarily those of The Maritime Executive.